taimuraamer
Hardware Root Of Trust: What You Need To Know Entrust
Root of belief establishes the safe course of boot up chain, called “Chain of Belief”, used to validate software program and hardware used on the system. If the credentials used to implement the preliminary piece of code are verified, every successive piece of code executed is trusted. A robust root of belief consists of id and cryptographic keys rooted in the hardware of a device. This establishes a novel, immutable, and unclonable id to authorize a tool in a community.
Safe Boot Defined: Root Of Belief And Chain Of Belief
- Hardware protection comes in more than one kind and choosing the incorrect one might imply compliance gaps and sudden publicity.
- Typically, a root of belief is solely the source a cryptographic system trusts by default.
- A platform root of belief is the first reliable anchor in the startup chain.
- The wolfCrypt Crypto engine is a lightweight, embeddable, and easy-to-configure crypto library with a robust give consideration to portability, modularity, safety, and feature set.
Every cryptographic key an organization relies on has to be generated and saved someplace. If a software program keystore runs on the identical server as the appliance it protects, the key is only as secure as the working system around it. Safe Boot is binary — the firmware both passes verification or it doesn’t. Measured Boot creates an in depth log of every component that loaded, allowing a distant verifier to evaluate the precise configuration of the gadget.
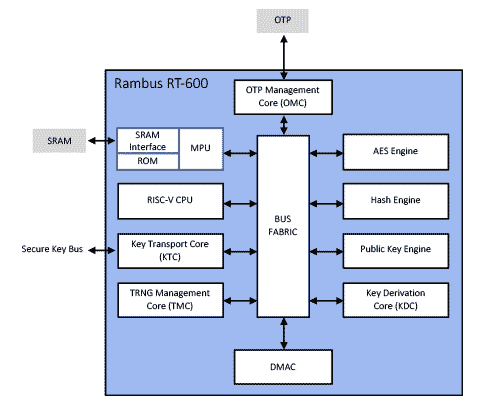
The Root-of-Trust is used to validate all the extra pieces of software that load on the system and is the primary foundational hyperlink in a Chain-of-Trust that efficiently boots an embedded system. The Root-of-Trust cannot be tampered with, which then allows the system to detect if software loaded later could be trusted or not. Builders must be in search of microcontroller solutions that have a hardware-based Root-of-Trust constructed into them.
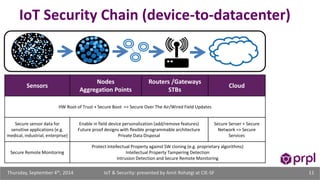
Iiot Results In New Safety Challenges
When the kernel has been verified, the firmware palms management to the operating system, and secure boot has accomplished its job. The system has started utilizing solely software program whose signatures were validated at every stage, so the operating system begins from a identified and trusted state. Duty for security then passes to the working system and the instruments running on it. The identical capabilities that safe the boot process can even safe the software-update course of, preserving methods within the subject from being tricked into accepting malicious updates. Software Program updates can be delivered through an encrypted tunnel using our processor’s community encryption hardware or delivered in the clear with an attached digital signature validated by our processor. Both mechanism can serve as proof that the replace is trustworthy and subsequently executable.
Safety
An HSM or TPM holds the signing keys that validate each stage of the boot course of, from firmware via the working system loader. If that hardware anchor is compromised, each validation step above it still stories success, so the failure goes undetected. On Home Windows techniques, the firmware verifies the Home Windows Boot Supervisor, which carries the verification ahead to the kernel. The kernel and its signed drivers are checked the identical way earlier than they load, so a tampered bootloader or an unsigned kernel will fail the check and forestall startup. This step issues as a result of the bootloader and kernel run with very excessive privilege, and code that loads at this stage might in any other case compromise the entire system earlier than any security software is lively. The root of belief holds, or holds the cryptographic hash of, the general public key used to confirm the first piece of firmware that runs.
Pki And Certificate Authority Protection
Secure boot defends against this by verifying the bootloader’s signature earlier than permitting it to run, which means a tampered or substituted bootloader will not https://californiarent24.com/smart-contract-audit-main-advantages-and-features.html move the verify. This safety is important as a outcome of a compromised bootloader can load additional malicious code whereas showing to start the system usually. Although the primary thrust of the hardware root of trust is to address the first two principles, it also addresses other ideas.